AI logs can become a second copy of your sensitive data. Govern what enters them before it reaches storage.
This case study revisits a disclosure from January 29, 2025. It is not a report of a new incident.
What happened
Wiz reported an internet-exposed ClickHouse database belonging to DeepSeek that could be accessed without authentication. It contained more than one million log entries, including plaintext chat history, API keys, and backend operational details and metadata. DeepSeek secured the exposure after Wiz disclosed it.
The reported count concerns log entries, not a verified number of affected people. The disclosure does not establish that the exposed records included medical or financial nonpublic personal information.
Two boundaries to protect
The incident illustrates two separate questions: who can reach a log store, and what sensitive material has already been copied into it?
Database authentication, network restrictions, transport security, and appropriate access permissions remain essential. ClickHouse and Wiz's subsequent guidance discusses these database protections. Application logging controls complement them by reducing selected sensitive contents before those contents reach storage.
Start with one AI application's logging paths. Inspect normal events, exceptions, SDK output, and fallback paths. Prefer useful operational context over raw conversations or credentials. Test with synthetic sensitive values and inspect the actual stored output, including behavior when policy evaluation fails.
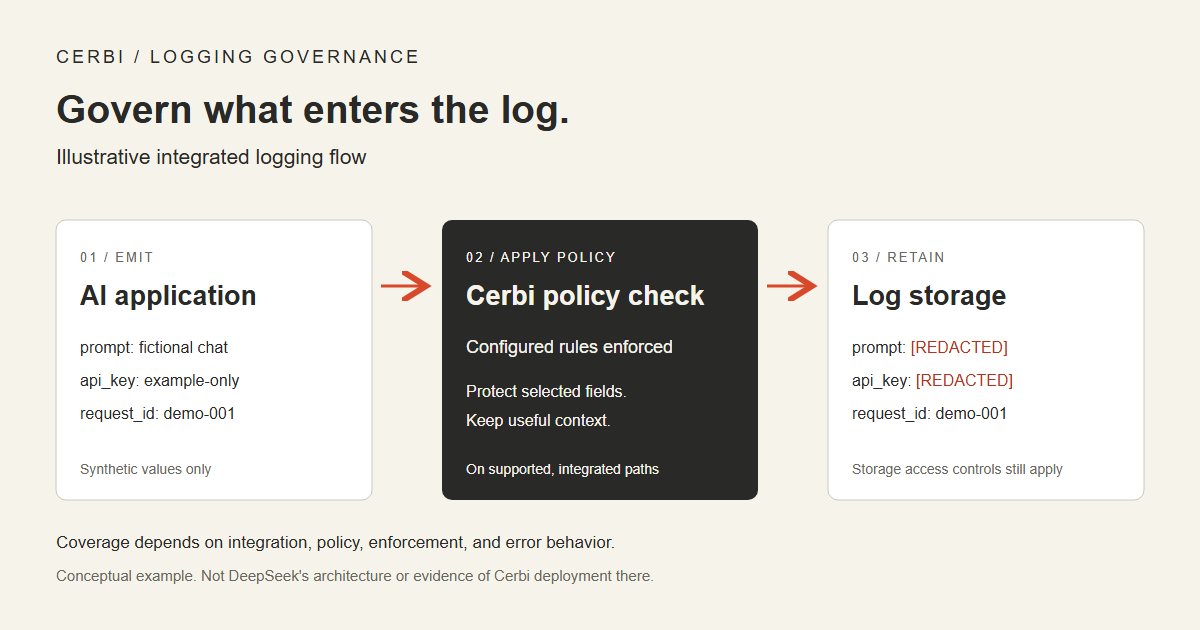
Illustrative integrated logging flow. Configured rules enforced. Fictional fields show a possible governed outcome, not DeepSeek's architecture or evidence of Cerbi operating there.
Where Cerbi can fit
Cerbi can help reduce sensitive contents on integrated application logging paths, where the relevant integration supports the desired action and its rules are configured and enforced. The diagram illustrates that conditional fit: a policy check changes selected fields before forwarding the event to log storage.
Coverage must be demonstrated on the paths you connect. An uninstrumented path, a missing rule, relaxed enforcement, or an evaluator error can change the outcome. Validate the integration's error behavior and review what actually reaches the destination.
This is not a claim that Cerbi would have prevented the DeepSeek incident, removes all sensitive data, or controls an external AI provider's internal logs. It also does not replace database security or establish regulatory compliance.
Test one workload
Choose one logging path and define which fields must remain useful, which require protection, and what evidence would demonstrate the result. Run representative synthetic events through normal and failure cases, then inspect storage and recorded policy outcomes.
Review your logging controls with Cerbi, or start with the free logging risk scan. Compare existing controls first and evaluate a supported integration where a specific gap remains.